
Making Cryptography Visible — and Quantum-Safe Migration Manageable
Telecommunications networks depend on cryptography across software, hardware, network functions, interfaces, protocols, devices, and supporting infrastructure.
As the industry prepares to transition to post-quantum cryptography (PQC), one of the first challenges is understanding where cryptography is being used today.
Operators cannot effectively assess cryptographic risk, prioritize migration, or replace vulnerable algorithms without knowing what cryptography is deployed, where it is used, what it protects, and what systems depend on it.
You cannot migrate cryptography you cannot see.
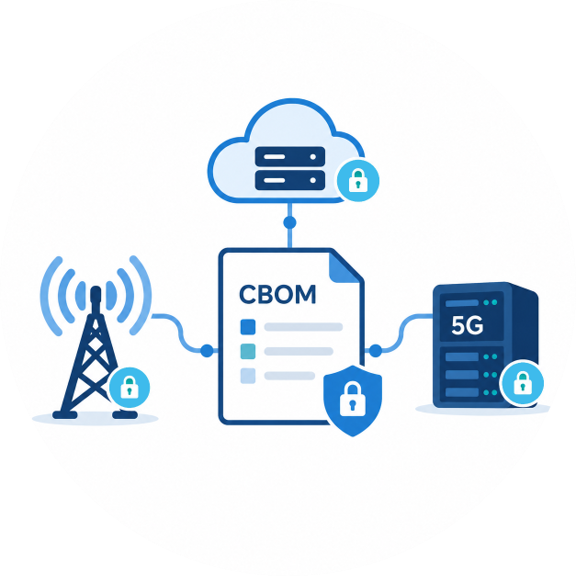
A Cryptographic Bill of Materials (CBOM) provides that visibility.
Why Telecom Needs a Common CBOM Approach
Generic cryptographic inventories alone do not capture all of the information needed to understand cryptography in a telecommunications network.
Telecom environments include network functions, standardized interfaces, protocols, security mechanisms, vendor implementations, and dependencies that need to be represented consistently.
Without a common industry approach, different suppliers and operators may describe the same cryptographic capability in different ways. This makes CBOM information more difficult to exchange, aggregate, compare, and automate.
A common telecom CBOM approach can provide a consistent way for operators, suppliers, technology providers, and government stakeholders to identify and understand cryptographic dependencies across complex communications infrastructure.
The goal is interoperability: enabling cryptographic information produced by different organizations and tools to be understood and used consistently.
ATIS Telecom CBOM Work
Through the Quantum-Safe Communications and Information Initiative (QSCII), ATIS is working with its members and the broader telecommunications industry to develop a common approach for creating consistent, interoperable CBOM for telecom services.
At the center of this work is the ATIS Telecom CBOM Profile, which defines how cryptographic information should be represented for a telecommunications service, together with a Telecom Property Taxonomy that provides a common set of telecom-specific properties and terminology. Together, these resources provide a structured way to describe where cryptography is used, the network functions and interfaces it supports, and the associated algorithms, protocols, certificates, keys, and other cryptographic dependencies.
The first implementation applies this approach to the 3GPP 5G Core Network, providing a common CBOM model for representing cryptography across 5G Core network functions and service-based interfaces. This establishes a foundation that can be extended over time to support additional telecom services, network domains, and use cases.
The open-source project also includes a validator and example CBOMs to help organizations create and test CBOMs against the ATIS Telecom CBOM Profile and taxonomy.
Explore the ATIS Telecom CBOM Profile, taxonomy, validator, and examples on GitHub
Learn more about why CBOM is important to telecommunications and how cryptographic visibility can support PQC migration and crypto-agility.
Part of the ATIS Quantum-Safe Communications and Information Initiative
The Telecom CBOM work is part of the ATIS Quantum-Safe Communications and Information Initiative (QSCII), which brings together industry stakeholders to address the technical, operational, standards, and migration challenges associated with securing communications networks for the post-quantum era.